You must log in or register to comment.
Specific to the Threadiverse, not the Fediverse, I’d like to have syntax to refer to posts and comments in a home-instance-agnostic way (so I can link to a post or comment in such a way that someone following the link stays on their own home instance), and I’d like to make it easier to link to groups in a home-instance-agnostic-way (
!community@instanceisn’t obvious to new users not familiar with the Threadiverse).IIRC, PieFed rewrites links to other Threadiverse instances to point to the home instance. That has its own problems, since sometimes (e.g. when doing technical troubleshooting), one wants to specifically link to a post on a particular instance.
I think that maybe the best fix would be on the client side, at post time, to look for links to other Threadiverse instances and offer to convert them at post time to host-instance-agnostic links.
On a related note, I think that the separation between usernames and display names creates problems in referring to users. As things stand, referencing a user must be done with
@user@instancesyntax. However, a user can have entirely-separate display name. One prominent example that probably many might be familiar with is @[email protected]:username: [email protected]
display name: 🇰 🌀 🇱 🇦 🇳 🇦 🇰 🇮@pawb.social
He chose a display name that looks similar to his username, just with a bit of Unicode styling…but there’s no technically-enforced requirement that a user actually do so. A user can make anything they want show up there.
The problem is that this makes it harder to learn or remember usernames to do
@user@instancereferences, and given that I think that a lot of Threadiverse users aren’t familiar with this functionality, it creates potential for impersonation or similar problems. Unicode has historically been vulnerable to similar-characters attacks when used for identifiers.I’d just drop the display name functionality.
Enforce web accessibility.
Bluesky and other parts of the fediverse like mastodon do this well.
Some communities do it better, but lemmy instances overall do not.
Lemmy users consistently show they do not get it, defend panaceas that do not fulfill web accessibility, and respond with hostility when it’s pointed out that inaccessible content is a systematic failure of will (poor choices of client & execution), not of capacity.I mean, inline images are kind of trouble brewing for accessibility, since you’re going to create problems for blind users. Yeah, okay, alt text can help, but not all users are going to write alt text (and I…don’t actually think that Threadiverse Markdown has a convention for adding inline image alt text at all, though I guess you could stick a manual caption beneath each image). AI image recognition and generation of descriptions is neat, but it’s subject to the limitations of AI models, and someone has to be spending compute resources running it.
If I were going to try to structure an environment to be accessibility-friendly, I’d probably just omit inline images. I happily used Reddit for a long time when there were no inline images, and have used other forums that don’t support inline images. That’s doable. But…I think that a lot of users do want inline images. I was just reading some discussion on the Threadiverse in the past week or so with someone saying that the reason that they didn’t like gopher/gemini was because they don’t support inline images.
hot take: we should make people have to use tone indicators
to help those who cannot understand or have conditions
You’re a condition
/s
that maybe disrespectful for me
Awards for the most prolific posters. With a cash prize of a zillion bucks.
It needs more normie content.
Universal login would be a killer feature. But I get it, each platform has its own “user” type so it would be difficult to do.
But imagine using your mastodon handle to log into piefed/lemmy, then same account post your video on peertube, etc…
It would stop being about the platform and more about the individual account.
i think it may work like this
for example
if you make an account on pixlefed.social you can log in to it on lemmy.world but here is the thing:
the content that you make on lemmy is put onto the lemmy.world servers instead of the pixelfed.social
so 2 accounts in one (that maybe a bad one)
Nomadic/portable identities. There’s a fep out there somewhere that proposes we’d be able to sign in to pixelfed/piefed/masto/bookwyrm etc with a single portable identity, and wouldn’t lose our identity and data when an instance went down. Imo, it’s the single most important feature we never managed to get implemented, since it fixes the single biggest barrier to fedi adoption: instance selection on signup.
That would be sooooo nice. I have so many accounts thrown around everywhere. Its hard to keep up with. And posting would be so much nicer.
I know a couple of fedi services have tried, but I just dont like their interface. piefed/lemmy is my favorite, followed by gotosocial/mastodon.
yeah I would be happy with something akin to saml but I agree here is would boost a lot of engagement in that folks would use othere areas of the fediverse more casually.
Ninja edits. A 30-second grace period to edit a comment before it’s marked as edited. It’s for fixing typos.
I have fat thumbs and almost every comment I make is edited.
I edit my comments like mad, but I think that showing the last modification time, which is presently done, mostly solves the problem in a better way than just a binary “edited or not” flag with a delay.
I believe that the reason you need to show that a comment has been modified is to deal with two problems:
-
Putting a popular comment in place, letting it accrue a lot of upvotes, and later editing it to contain wildly different content. This gives the new content unwarranted credibility.
-
Writing a comment, waiting until someone responds, and then editing the parent comment so that their content is placed in a different light.
Having a comment last-modified time does a better job of solving #2 than a binary “edited or not” indicator (since one can see whose comment was edited most recently).
One can’t always infer enough information to address #1 from just a last-modified time, but generally, one that’s way out-of-whack from surrounding comments in modification time is a red flag.
I think all of the clients I’ve seen just show the last-modified time, and I don’t know if the API exposes both original and last-modified time.
searches
Apparently yes.
https://www.socialfetch.dev/docs/api/v1/lemmy/post/comments/get
You have the “publishedAt” and “updatedAt” times.
So clients have all the information they need to know how long a comment stood between initial publishing and last modification. You could maybe just have clients show the delta between publishedAt and updatedAt. That’s a superset of what a boolean “edited after grace period” indicator shows.
-

Pretty sure Mbin has that, let me test. Edit.
Magic!
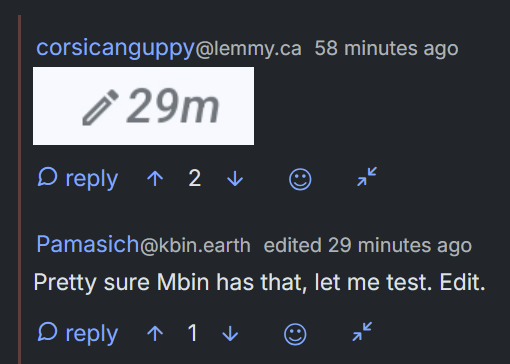
Tried fetching the JSON-LD, don’t see the
updatedproperty on it like with remon’s Lemmy test which does have it.I see the edit marker on piefed.
Pretty sure lemmy has that.
edit: test
“updated”: “2026-11-15T16:09:27.187394Z”
Does seem like Lemmy, unlike Mbin, records that information. And then it’s up to each client instance to honor or not honor the ninja edit window.
Shows as edited for me, at least.
Not for me.
I’d like cross platform polling. I know Piefed has polls, but if it doesn’t carry over to people not on Piefed, it’s not so useful.
I use comment upvote counts to run my annual community polls for people to choose A/B, but I wonder how much influence it bias it has on people when they can see totals before voting.
You can use an offsite polling site and link to that. There are a number of “run a poll” websites out there.
EDIT: e.g.
I’ve been unsure if redirecting people away from their instance’s page or app would be a friction point for people. Fediverse people can feel a lot more “particular” about any number of things, and I use our annual poll series somewhat as a recruiting drive to grow the community, so I want it to be as smooth as possible for anyone coming in for the first time.
I’ll check out the sites you provided. I’ve looked at a few before, and while I think they’re pretty painless, I’d want to get some community feedback, though again, it’s new users and lurkers I’m trying to capture, so I may still not get feedback from the people I’m actually invested in getting participation from.
It’s also about 30 polls I run in a 2 week span (I’m running a bracket tournament popularity contest) that’s still 30 extra things I’d have to do as well.
Having it be a native feature would negate all those points, especially for things that are out of my hands.
Combining crossposts on every platform would be neat…
PieFed does this already. For instance, you can see that this article was posted 29 times and had a total of 159 comments:

And then when viewing the post, the comments are organized below into each community:

Note: The totals given for each community don’t seem to line up with the overall total. It might be a bug caused by deleted comments.
It would be nice if other platforms had the same kinda deal.
Its very hard to do in practice so I kinda get it.
Note that while I get the benefit, one historic mechanism for trolling on Usenet relied on the fact that many clients would respond to both Usenet groups if a post was cross-posted.
This meant that one could post troll bait cross-posted to two groups that had userbases that didn’t agree with each other, and watch as a flamewar ensued. E.g. “I’m thinking about getting a Mac or a Windows PC and am not sure which is better. I heard from my friend that Macs kind of suck. Can you help explain?” to comp.sys.mac.advocacy and comp.sys.ms-windows.advocacy or something.
Reddit avoided this by not having responses visible to users visible to both groups. It just linked to cross-posts.
PieFed’s merging of crossposts to users of both groups helps address federation-induced fragmentation on the Threadiverse (multiple “linux” communities effectively act as one ad-hoc community for the life of a given crosspost). But it also lets a malicious crossposter force users of arbitrary groups into one discussion, and I can say that that definitely led to problems in the past.
I noticed that the communities and accounts I have blocked still count towards the displayed combined total.
Also “combining crossposts” because most people don’t use that feature, and post in multiple communities instead (for Lemmy).
Photo Gallery for posts with multiple images.
So you can swipe through them instead of opening and closing them individually.Cryptographically signed messages. There’s no excuse for a platform where instance operators can impersonate their users in 2026.
While I like the idea of having keys, I think that it should be tied to a broader shift to “key is identity” over “username is identity” and would also provide cross-instance portability for if a user changes instances. Like, we’ve had Threadiverse instances permanently go down, and it’d be nice for people to be able to indicate in an authoritative way that they are the same user as a user on another home instance.
Mind, there is a key distribution problem that has to be solved — if you don’t trust a user’s home instance to map a username to their public key, who is authoritative as to their pubkey?
I mean, I could imagine other instances caching pubkeys and flagging changes and having a third-party client (not a Web UI provided by thr home instance) request their own pubkey via another instance and seeing whether it matches what’s expected as a best-effort to try to catch some impersonation attempts. But it’s not just a trivial drop-in.
EDIT: Also, it’s nice to have a backup account on another home instance, since that leverages one tremendous strength of the Fediverse — one instance might go down, but unlike, say, Reddit, it’s really hard to take the whole thing down. Reddit will beat lemmy.world’s uptime, but it won’t beat the Threadiverse-as-a-whole’s uptime. The downside of that today is that it’s kind of a pain for both the user (unless their client does a good job of “merging” accounts) and for other users (who have no way of knowing that the two accounts are actually the same user, and not just some imposter user). If users could just fairly-transparently fall back to a secondary account if an instance has downtime, that makes the Threadiverse as a whole more-resilient to downtime.
Yeah… Key distribution is hard. My natural inclination is to use something like ENS, but there’s no way anyone would accept that 🤣
There’s also one other issue that some instances presently rely on rewriting comments. Lemmy.today does so, for example: this is done to deal with a separate issue where one can cause a user’s IP address to be exposed. I raised the original privacy issue some time back and have more discussion there.
It’s possible for an attacker on the Threadiverse to send a direct message or a comment to a victim user that contains an inline image, where the image is hosted on a server that the attacker controls. The victim’s client or Web browser will then automatically load that inline image directly, handing the victim’s IP address to the attacker.
This was worked around on Lemmy by having the user’s home instance — if set up to do so — act as a caching proxy for inline images for users on that home instance, while rewriting the comment to point at the local proxy. That way, only the home instance’s IP address is exposed to a potential attacker.
That solves the problem exposing a user’s IP address. However, it also means that (a) the chain of trust is broken for the image, and (b) that because the comment is modified, even if the original comment were signed by the user, the comment body text would fail a simple validation.
In theory, as long as this rewriting were done in predictable ways, one could have validation of comments do a reverse transformation (converting a proxy link back to a non-proxy link), which would address (b), and I suppose that theoretically, a user could also include a cryptographic signature on files that they link to, which would address (a).
But if we start getting more automated rewriting of comments in a variety of ways and start relying on that rewriting, it’s going to become more-difficult to cryptographically-authenticate comments.
I don’t know what other Threadiverse server implementations, like Mbin and PieFed, presently do around exposing user IP addresses, whether they rewrite comments or not.
You could work around that by signing the hash of the attachment I suppose.
The UI for rewriting messages could be simple enough. You’d display the altered message with a signature from your home server, and have a “view raw” that displays the original signature?
Where would you keep the keys? In the browser?
Yes, that’s a decent option. Browsers offer pretty good keystores these days, and you could keep an encrypted copy on your instance (or use BIP39 seed phrases or whatever!)
If the browser is running js from the server to maintain and use the keystore, then it’s at risk from malicious admins. They can inject js to reveal the keys.
Keeping keys on the instance means the instance eventually decrypts them, which puts the user at risk of malicious admins.
It feels like the only way to make it work is with trusted apps that are independent of the instance admins.
That’s, surprisingly, not the case at all! You can make non-exportable keys. The instance owner could, theoretically, change the published key for an account, but that would be visible.
I have a small thing that bugs me on lemmy.

What does the chat button do here? Literally no purpose as clicking it just sorts by new. Please remove it entirely
One of those restaurant style food warming trays for beans
Also: free monthly beans deliveries.
Sharing a Lemmy post with links on Mastodon shouldnt redirect the person who clicked the link to the signup page of the lemmy instance the post was posted on, but it do.
I would love to be able to see all posts on a community across all instances. I.E. I want to browse c/Linux but see posts from any community named ‘Linux’ regardless of which instance it’s hosted on.